Iranian state-backed cyber actors are using a malware called Chosen Brick to target Windows users and steal personal information, according to a joint warning from U.S., UK, and Dutch intelligence agencies. The attacks often begin through WhatsApp or Telegram, where attackers impersonate trusted people or organizations before convincing targets to download files disguised as legitimate programs. Once installed, Chosen Brick can capture screens and audio, steal emails and social media messages, download additional malware, and even wipe the infected computer. Officials say Iran has used the malware since at least 2025, primarily against dissidents, activists, journalists, and others viewed i as threats to the Iranian government.
Why This Matters:
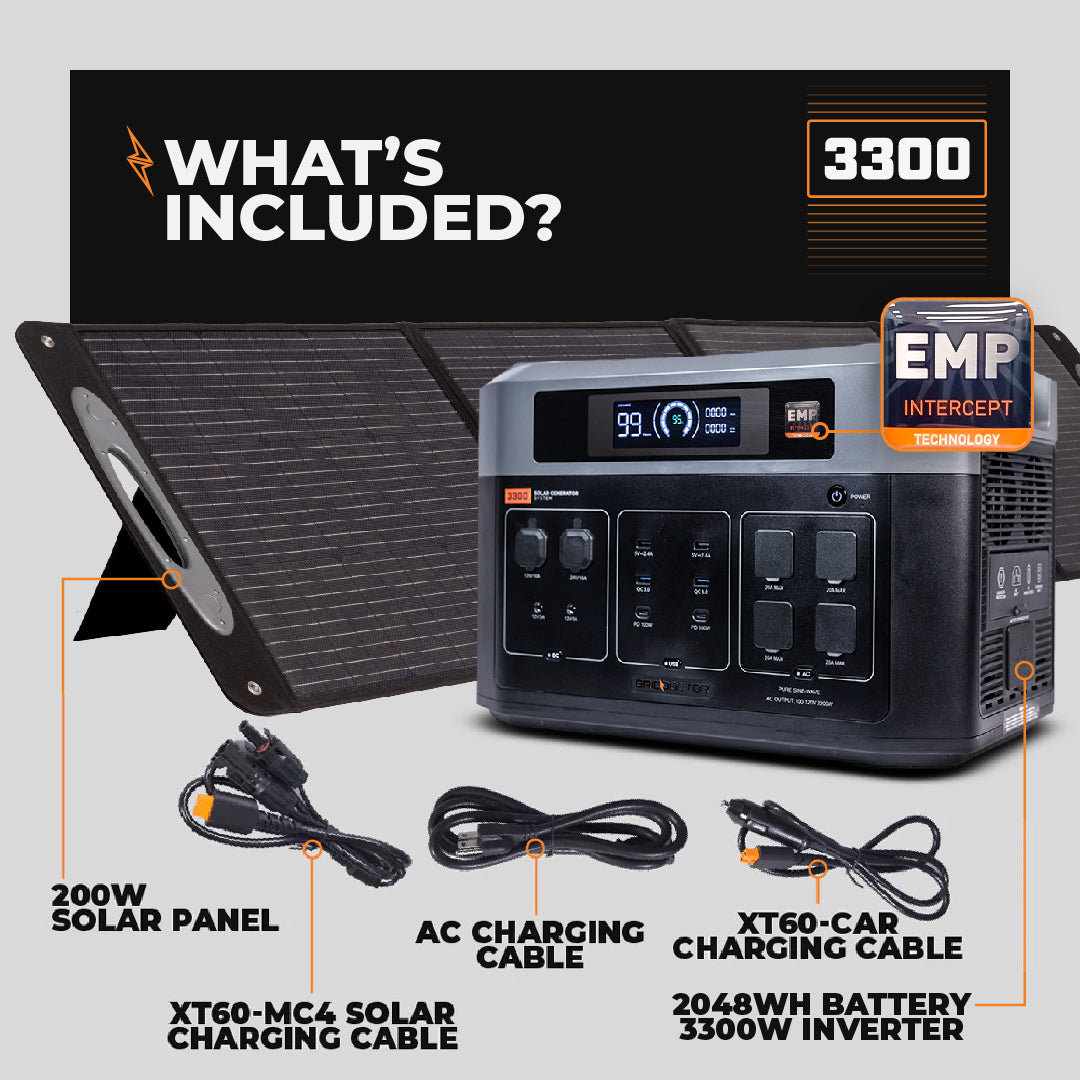
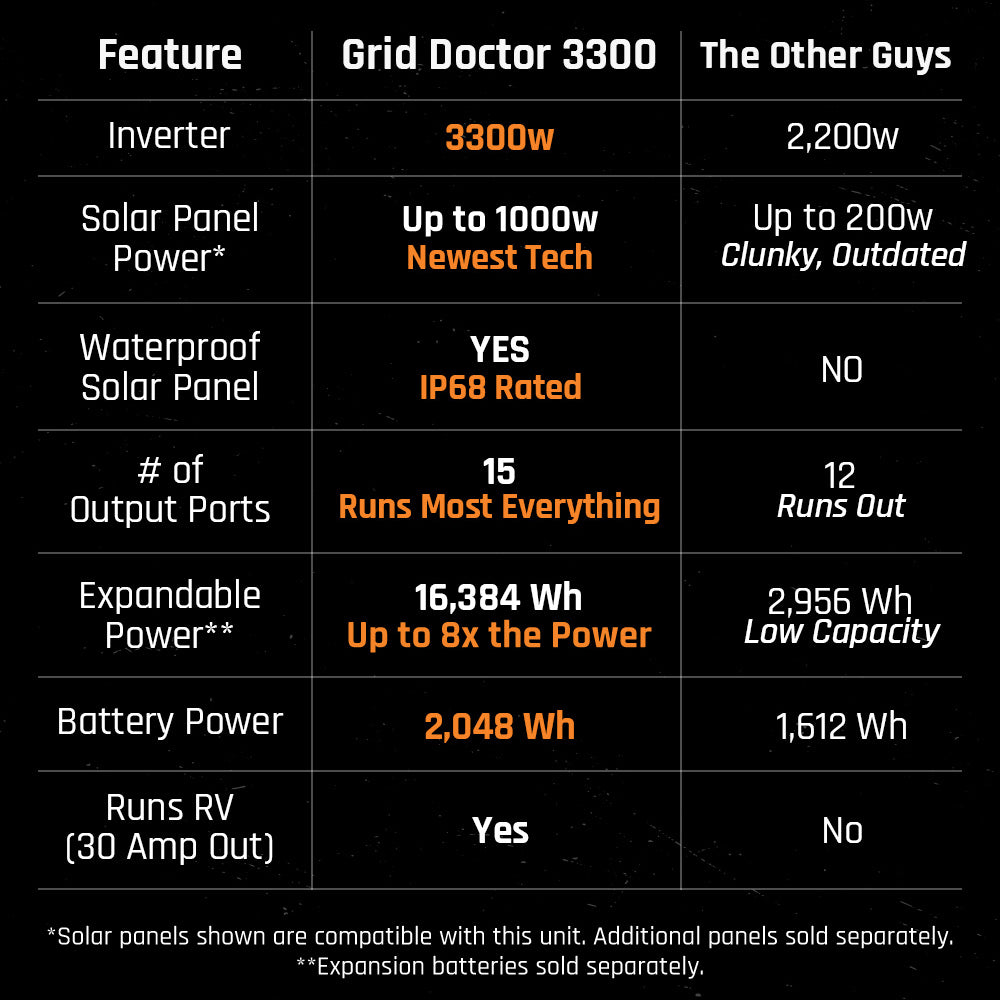
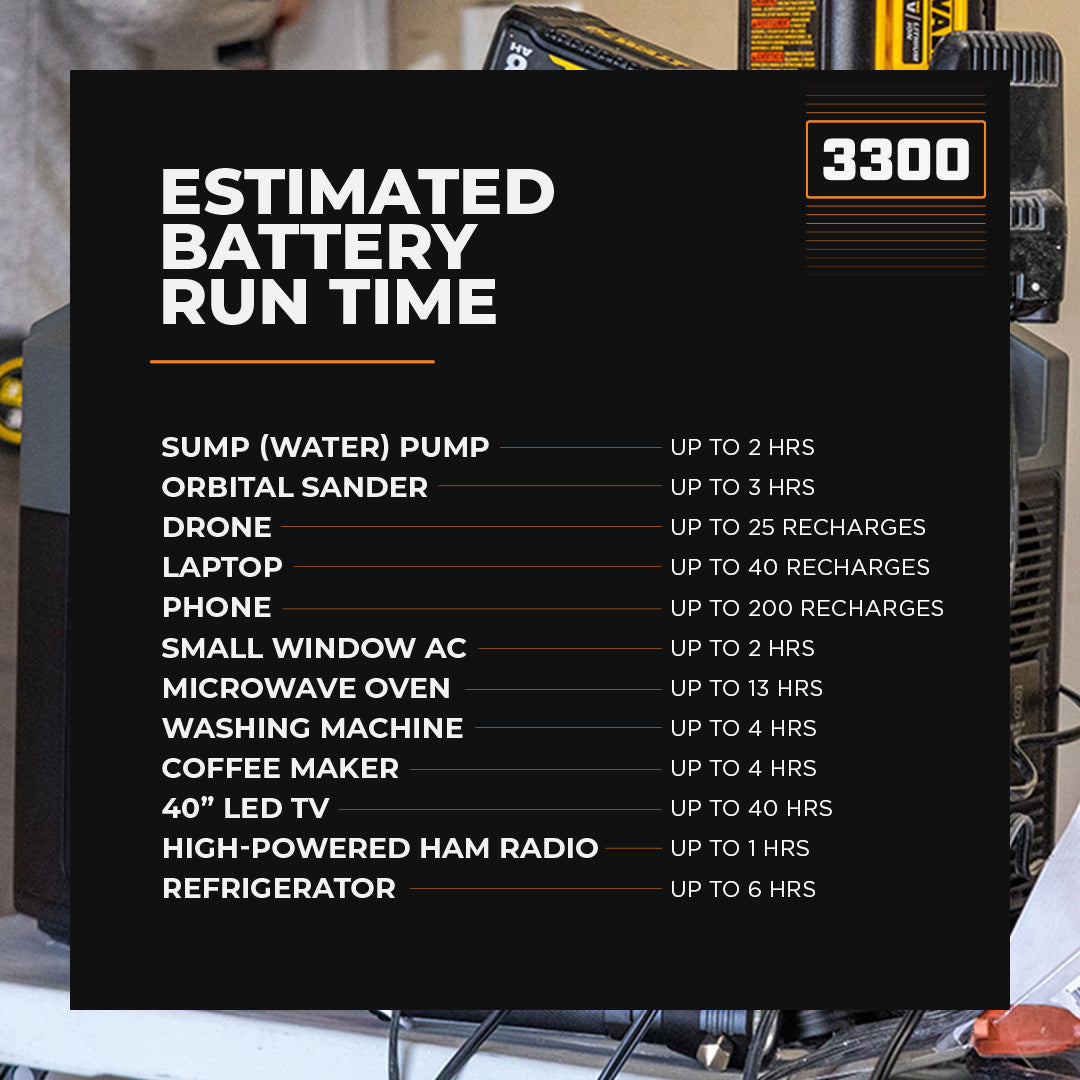
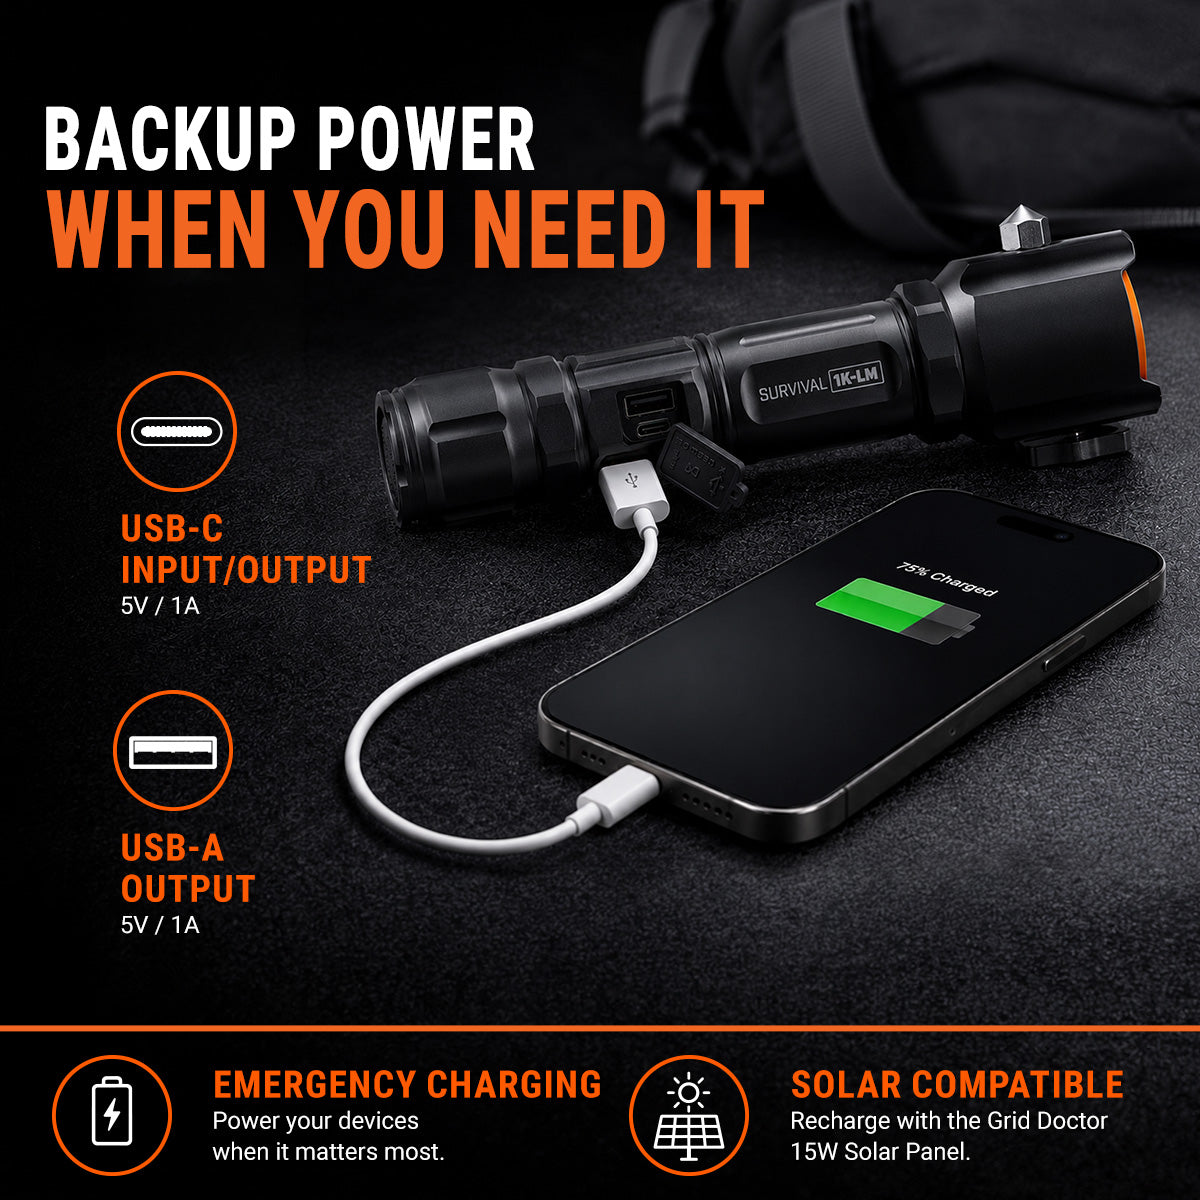
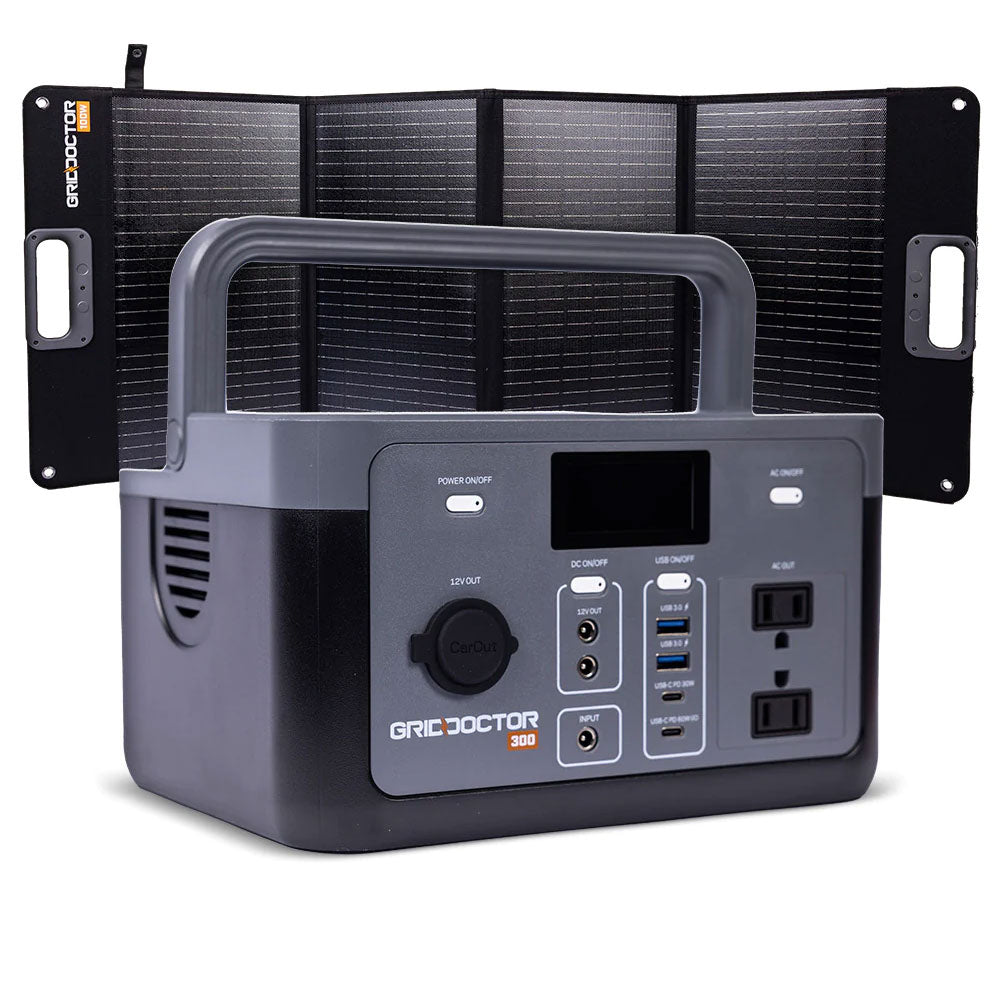
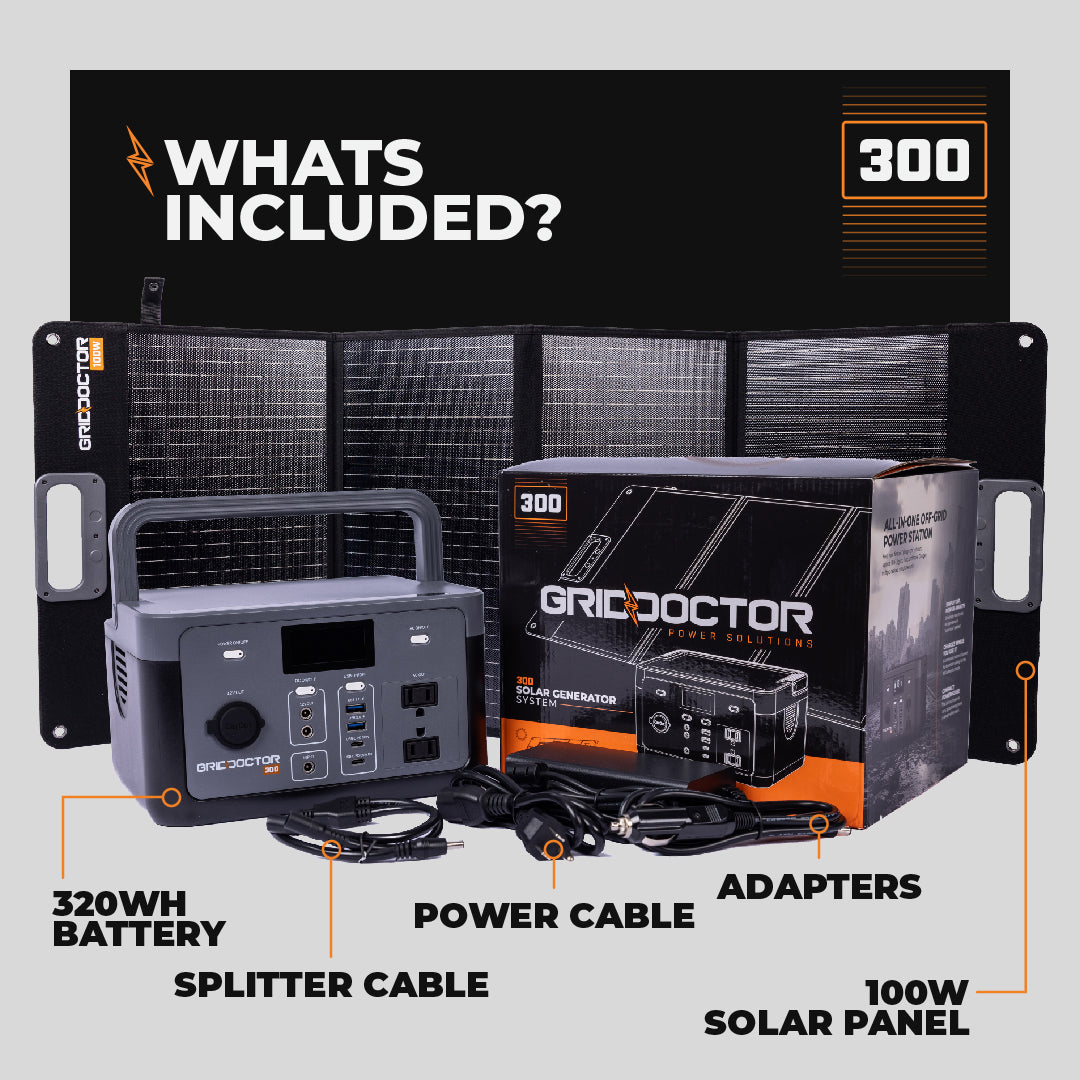
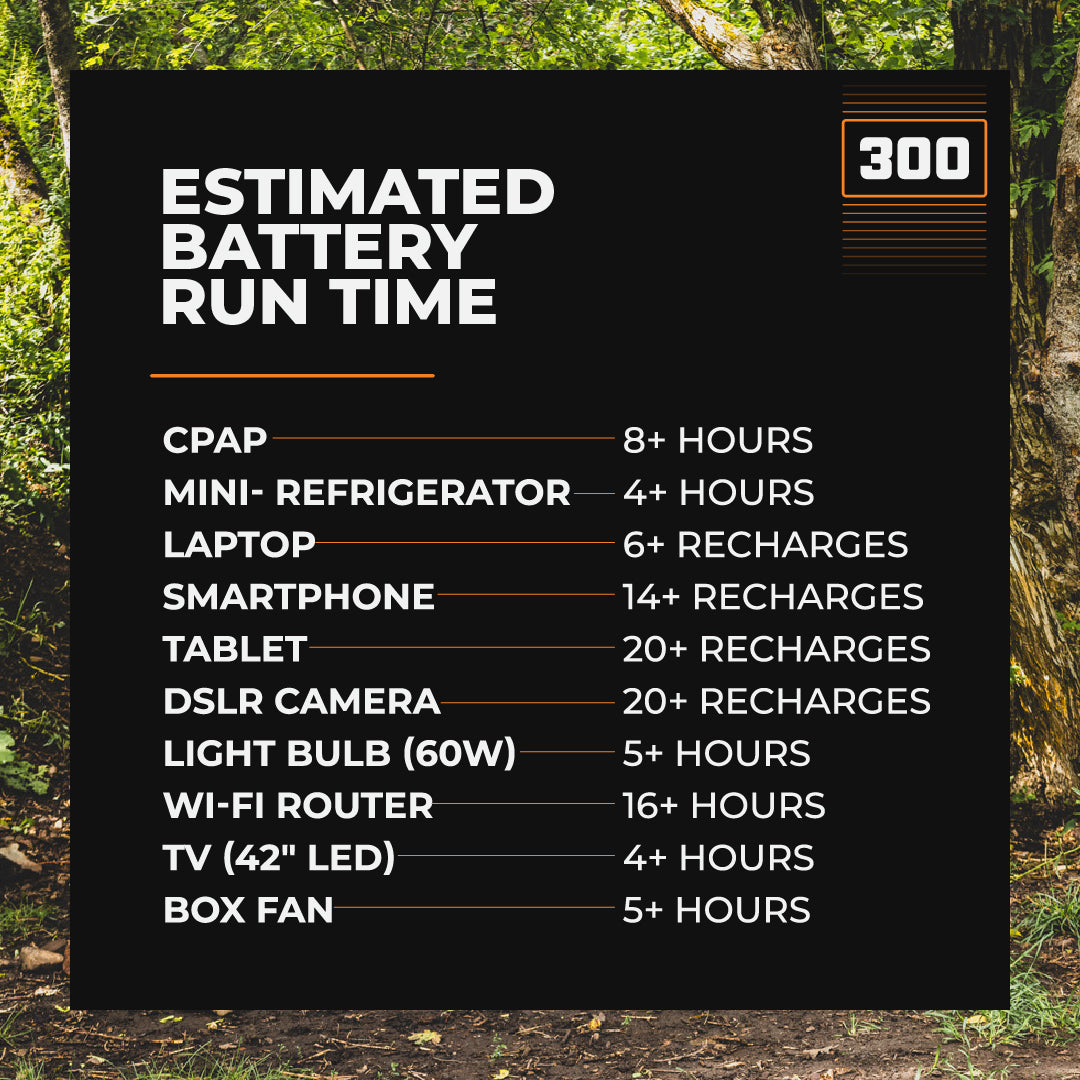
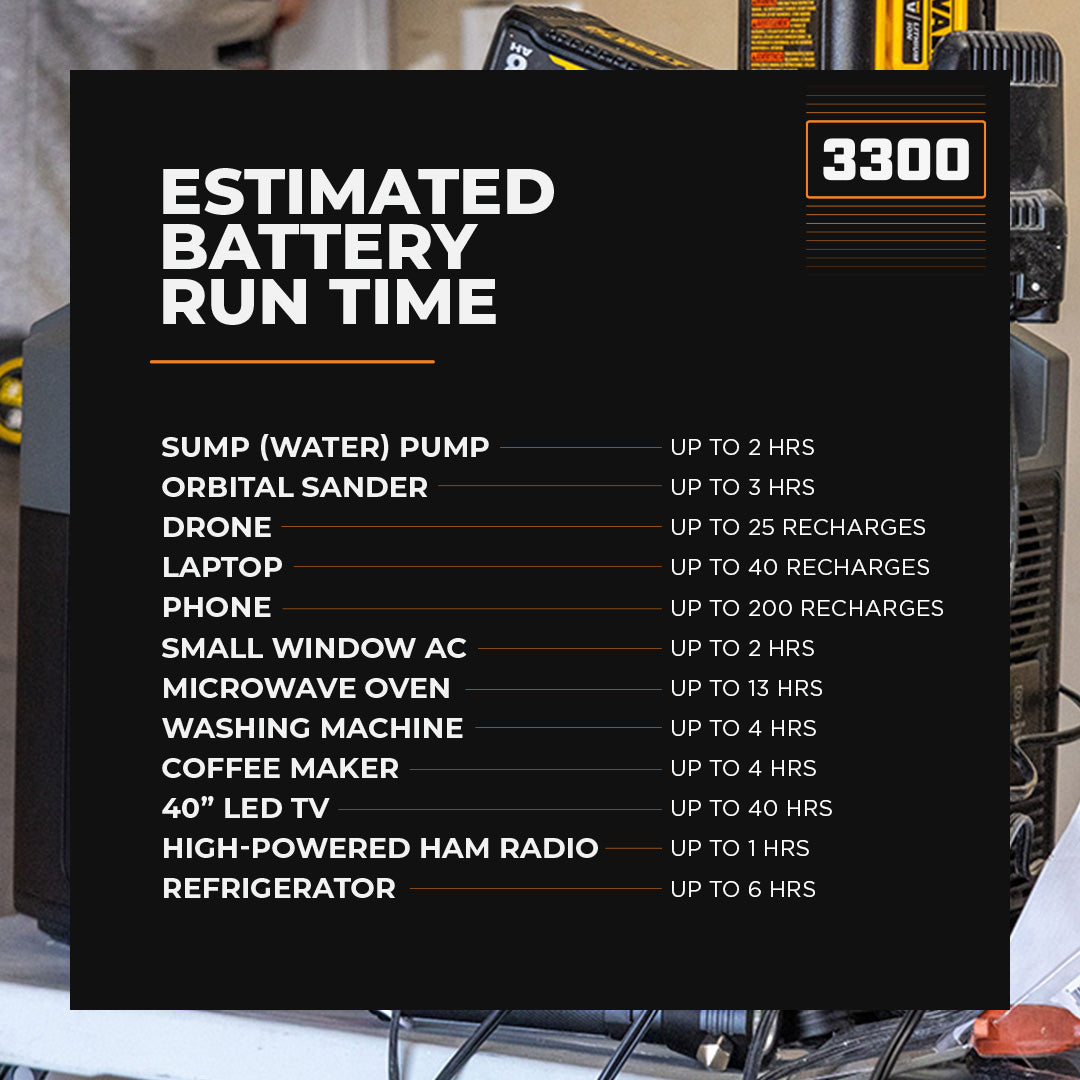
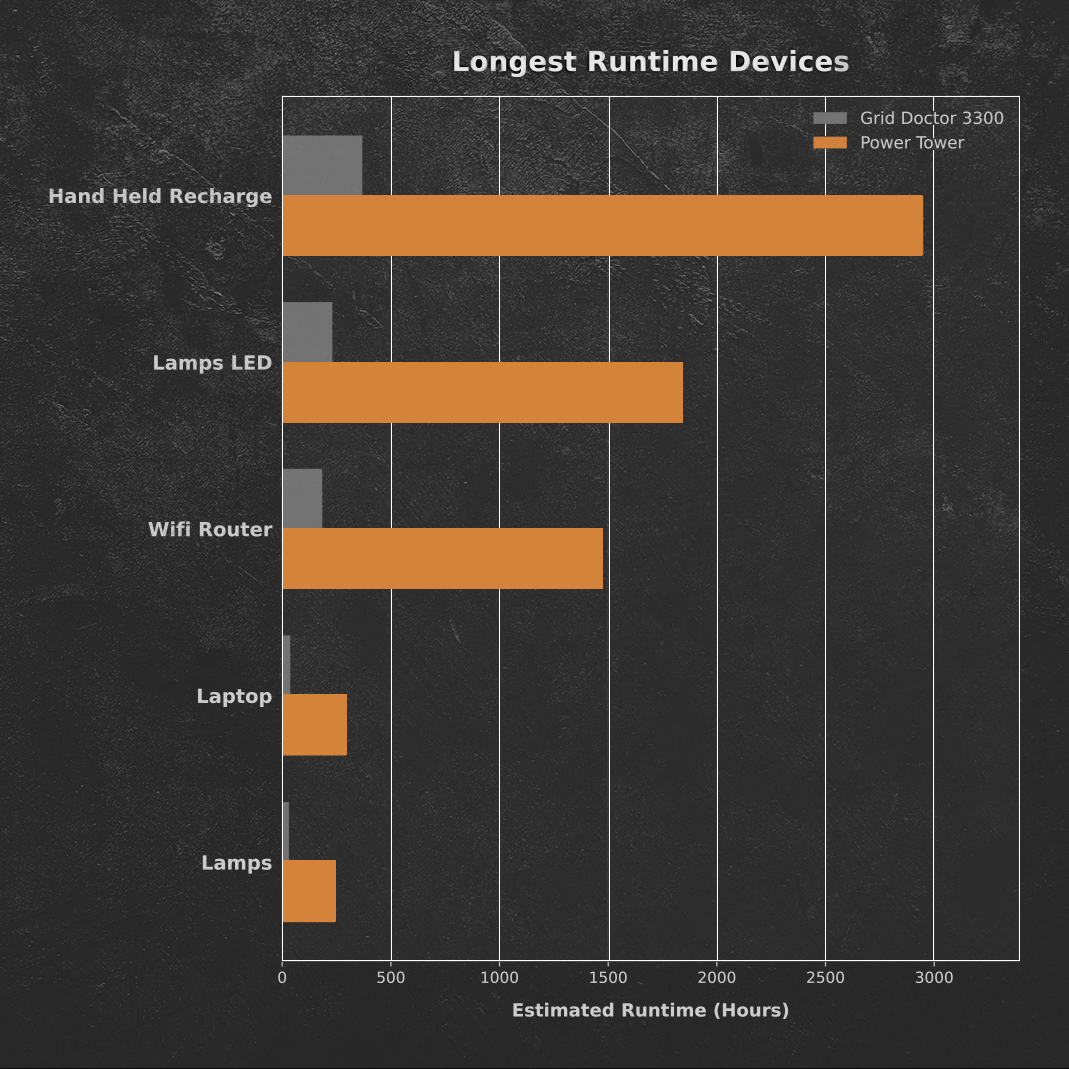
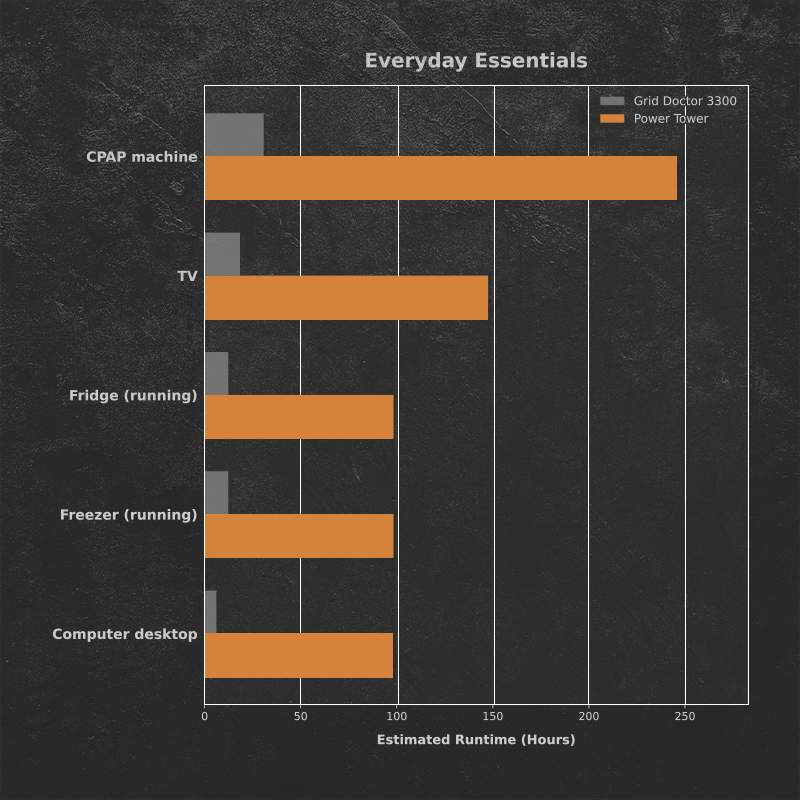
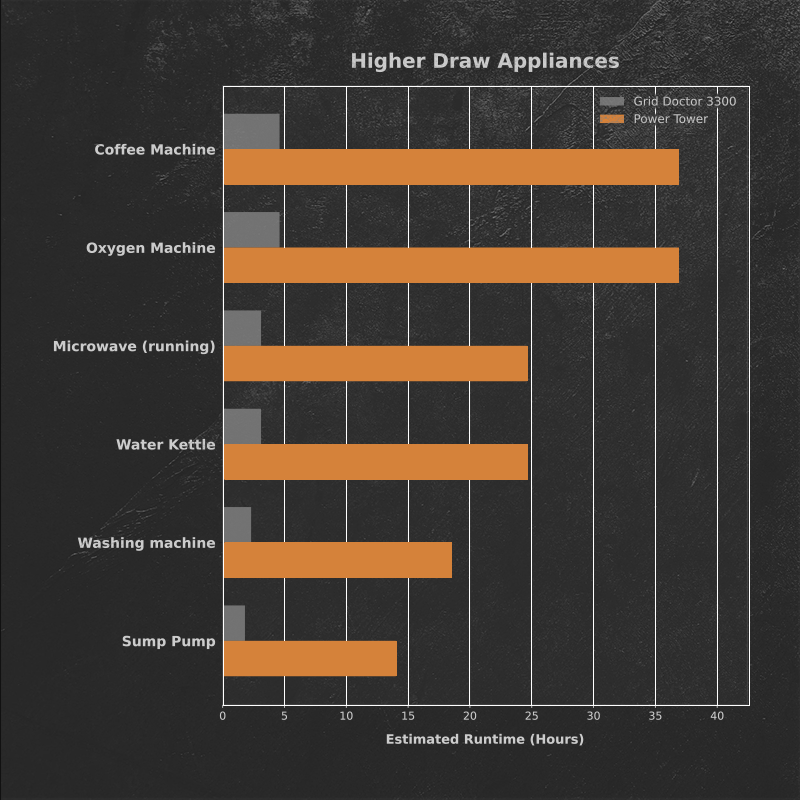
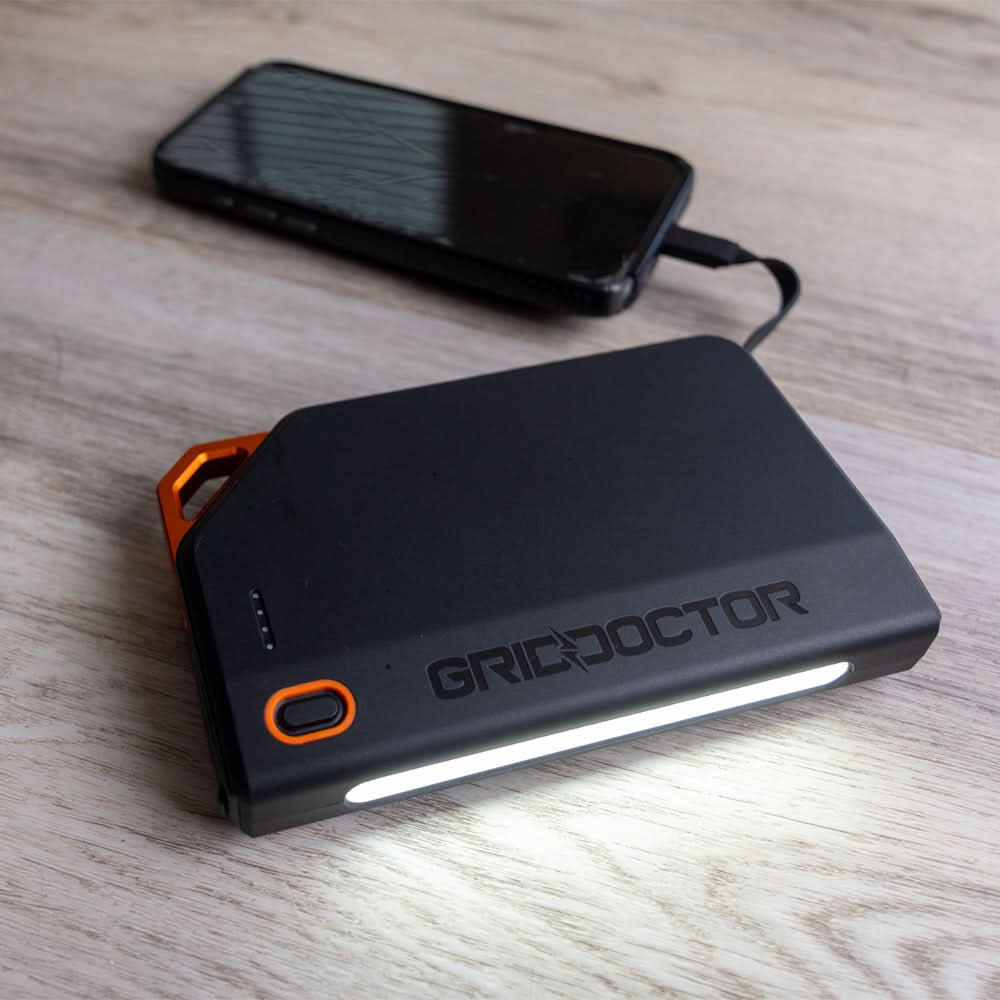
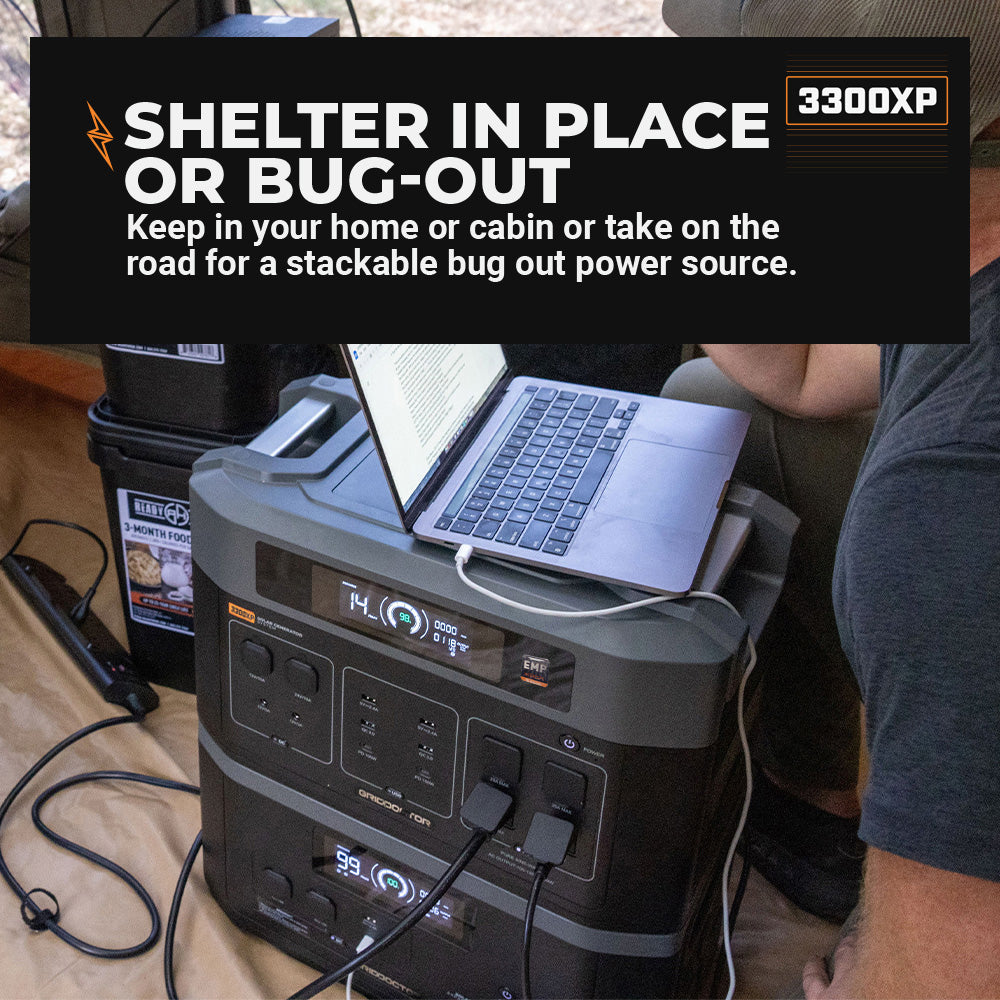
Chosen Brick shows how sophisticated cyber threats can move from distant geopolitical conflicts directly onto personal devices, using familiar apps and trusted contacts to get inside. The warning comes amid a broader rise in cyber activity affecting water, energy, manufacturing, and other critical systems, where a successful attack can create consequences far beyond stolen data. Cybersecurity is one part of preparedness, but households also need a plan for the physical disruptions that can follow an attack on essential infrastructure. Having backup power available can help keep phones, communications, lighting, and other essentials running if a cyber incident contributes to a wider power disruption.
Read the full article here.
Source: The Register
By: Jessica Lyons